Our Bots Don't Sleep.
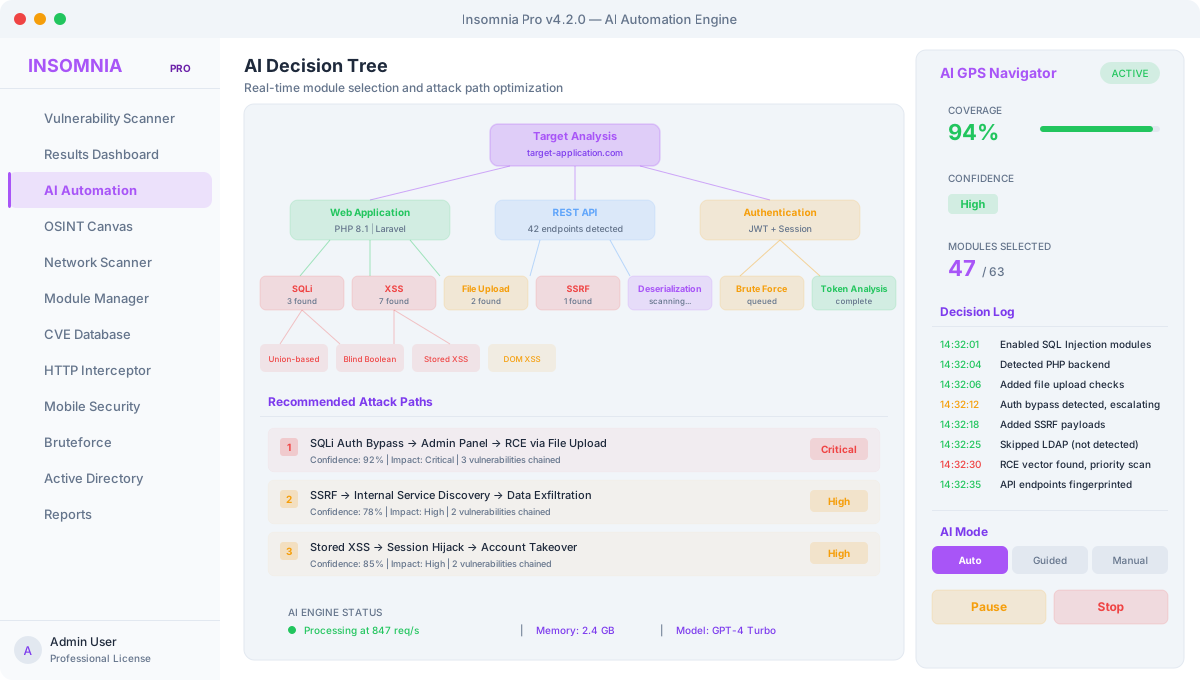
While your team rests, Insomnia Security Suite's autonomous AI red team crawls, fuzzes and exploits your apps, APIs, networks and Active Directory — around the clock. Grab the keyboard anytime, shift left with SAST + IDE, and ship it all hardened on Insomnia OS: one AI platform for pentesters, developers and students.
SAST Free static-analysis CLI — finds bugs before they ship $ pip install sast Explore CI/CD →
Add Insomnia to your CI / CD
Wire SAST, DAST, secret detection, container audit, and a deploy-gate into your existing pipeline. Free, customisable, and ships in 30 seconds via the online wizard — no SaaS, no signup, just one YAML.
See It In Action
Watch a full run — scan, AI triage, exploit and report, end to end.
Take Insomnia everywhere
From your editor to a drop box on the target network — the same engine, wherever you work.
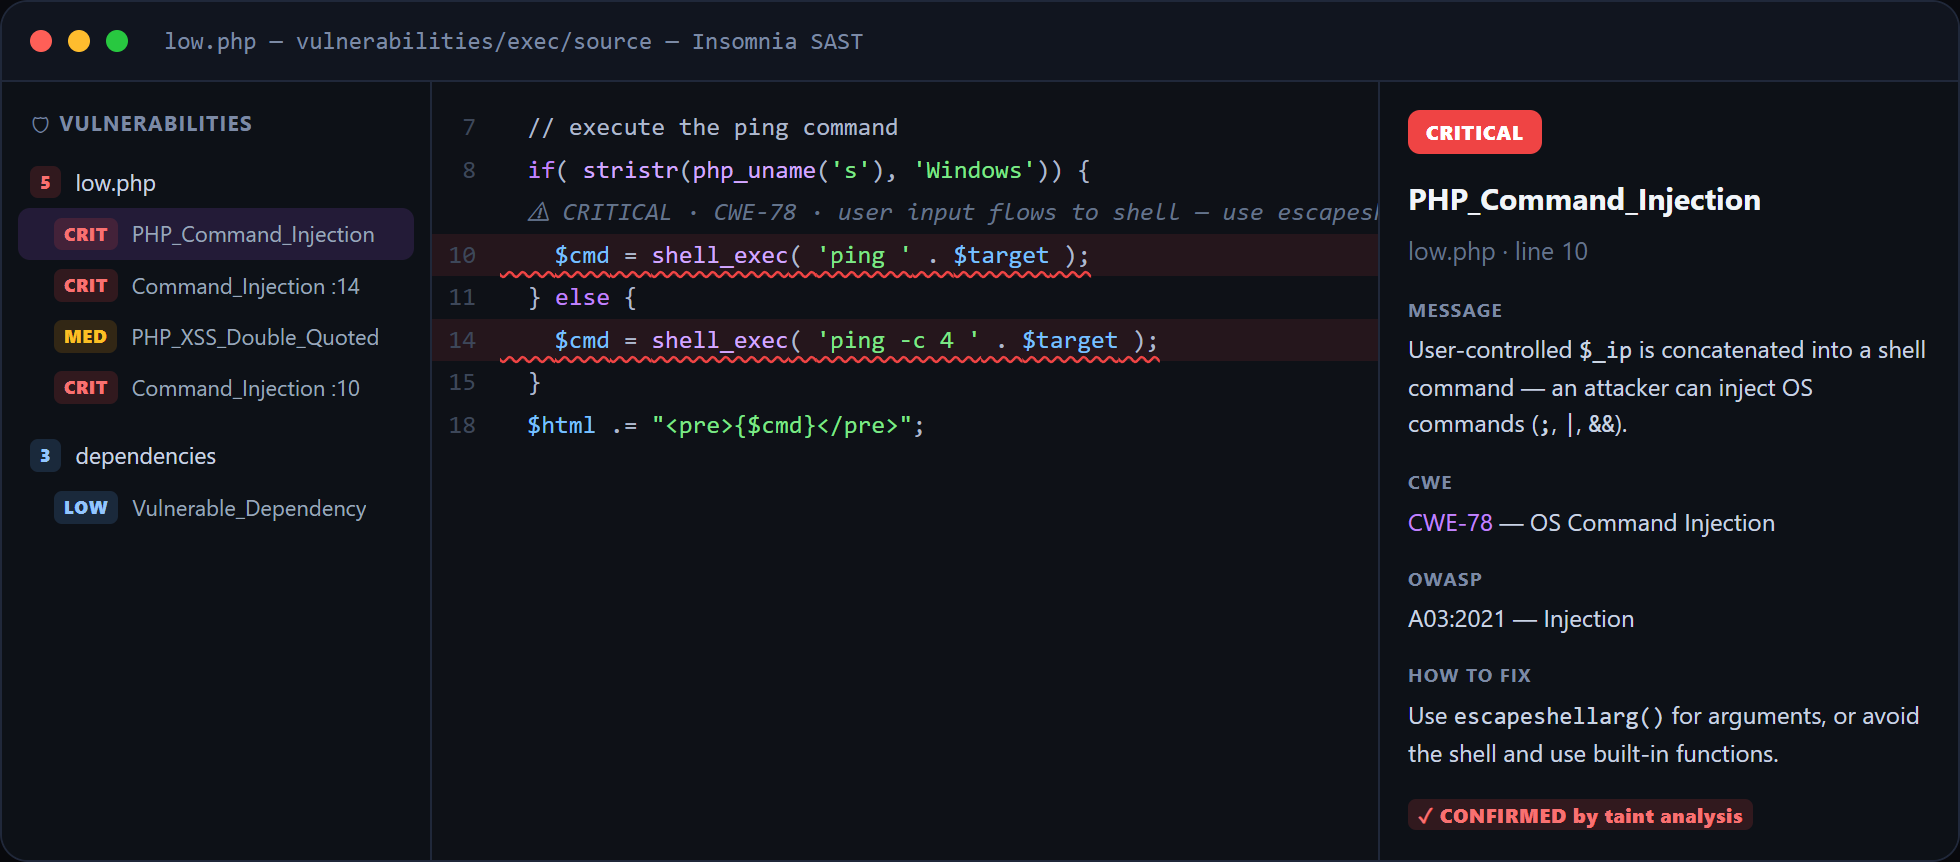
Catch vulns right in your editor
Insomnia SAST underlines secrets and vulnerabilities on the exact line you wrote them — confirmed by taint analysis, with CWE/OWASP and a one-click fix in the side panel.
Explore the plugin →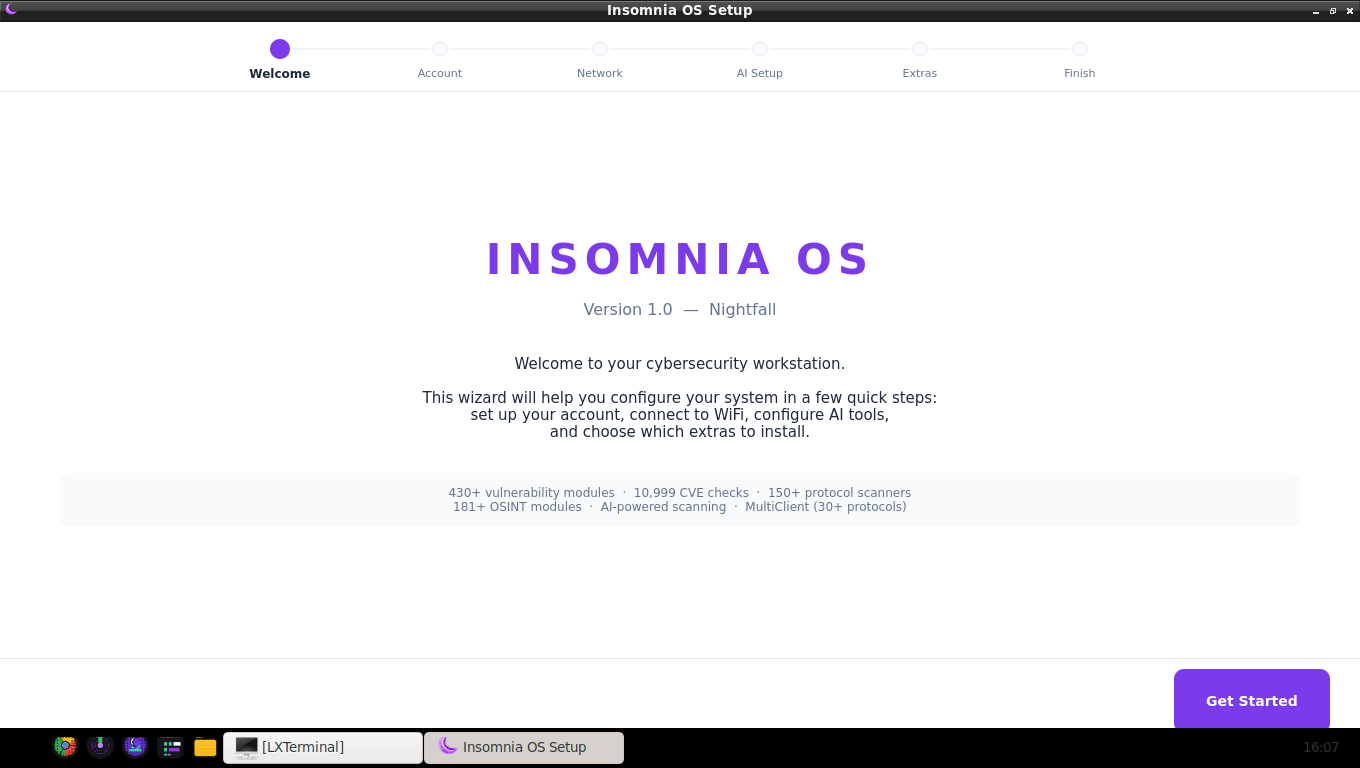
A full red-team OS — and a box to run it
A Debian-based offensive OS with the Insomnia scanner, 430+ modules, 11k+ CVEs and a complete red-team toolkit preloaded. Flash it for Raspberry Pi or x86 — or drop the plug-and-play Pi 5 appliance straight onto the target network.
Explore Insomnia OS →Run a full pentest from your phone
Open ChatGPT (or Claude / Grok) on your phone, connect it to Insomnia's remote MCP server, and just ask. Insomnia scans, finds real vulnerabilities, and can generate the report for you — then check whether a finding is actually true, send the HTML out, and let the AI validate it. No laptop needed.
- 1 Ask in plain English — "pentest my site."
- 2 Insomnia finds vulns and confirms them (no false alarms).
- 3 It generates a full report — and can email the HTML out.
- 4 The AI re-validates every finding so you trust it.
Complete Offensive Security Platform
Web, API, network, Active Directory, OSINT and source code — one AI-driven platform replaces the rack of single-purpose tools you used to chain together.
Web Vulnerability Scanner
275+ modules: SQL injection, XSS, SSTI, SSRF, LFI, RCE, deserialization, GraphQL, JWT, HTTP smuggling, and every OWASP Top 10 category.
AI Red Team (7 Agents)
7 specialized AI personas that actively probe with curl, nmap, and custom scripts. Mix Claude, GPT-4, Mistral, and Gemini across the team.
Network & Protocol Scanner
Port scanning, 20+ protocol-specific scanners (SSH, SMB, RDP, MQTT, ICS/SCADA), service detection, and 30K+ CVE matching.
OSINT Intelligence
Domain, IP, email, username, phone, company recon. Breach lookups, interactive visual canvas with 200+ transforms.
Active Directory & Creds
AD enumeration, NTDS audit, Kerberoasting, attack path visualization, lateral movement. Multi-protocol bruteforce.
Professional Reports
Executive PDF/DOCX reports with findings, evidence, CVSS scoring, remediation steps, and compliance mapping.
One Platform, Zero Compromises
Stop juggling a dozen disconnected tools, paying separate licenses, and stitching reports together manually.
- 5+ separate scanning tools
- Manual context switching
- No AI, no automation
- Stitch reports from multiple outputs
- Pay per tool, per seat, per year
- Weeks of training per tool
- 275+ modules in one platform
- Unified workflow, single UI
- 7-member AI red team runs scans autonomously
- One-click PDF/DOCX/HTML reports
- One license covers everything
- Productive in minutes, not weeks
Download Sample Reports
Real reports from intentionally vulnerable targets. Interactive HTML with full findings, evidence, and remediation.
SAST — Source Code
Taint flow, 230+ secret regexes, 12-ecosystem dependency audit.
DAST — Web App
Full crawl + 275 active modules: XSS, SQLi, SSRF, IDOR on a live target.
OSINT — Passive Recon
Subdomains, breach data, leaked creds, GitHub leaks, social mapping.
AI Pentest — Autonomous
AI-driven full pentest: 100+ findings, attack-path narrative, real PoCs.
Service Enumeration
SMB/LDAP/Kerberos/SNMP/NFS deep enum, null-session, AS-REP candidates.
Forensics & IR
Disk + memory triage, reconstructed timeline, evidence hashes, Volatility.
Network & Ports
TCP/UDP scan, service detection, banner-grab, CVE mapping per host.
Active Directory Audit
Kerberoasting, DCSync, ADCS ESC1, delegation abuse, BloodHound paths.
Host Auditor
SUID/sudo rules, kernel-CVE advisor, patch matrix, privesc path suggestions.
CVE Scan
Per-CVE CVSS v3.1 breakdown, CWE + OWASP mapping, safe-check evidence.
Mobile (APK / IPA)
Manifest perms, hardcoded secrets, SSL pinning, embedded native libs.
CI/CD Pipeline
7-step run: SAST + secrets + deps + DAST + container + deploy gate + Slack.
Why Insomnia Is Better: We Prove Our Numbers in Public
Other security vendors claim “industry-leading detection” on closed marketing datasheets without publishing a single raw scan report. We run Insomnia against 376 live containerized & source targets across 8 attack surfaces and publish every HTML & JSON scan report, every ground-truth proof, every missed case, and our exact ~6.0% false-positive rate.
Head-to-Head: How Insomnia Compares to Other Scanners’ Benchmarks
Single-domain scanners only test a fraction of your attack surface and hide their raw outputs. Here is how Insomnia compares against industry scanners across published benchmarks and our 50-repo / 376-target live lab:
| Scanner | Web / DAST | 1-Day CVEs | Network | SAST (Source) | API / GraphQL / MCP / Mobile | Avg FP Rate | Public Raw Reports? |
|---|---|---|---|---|---|---|---|
| Insomnia (v3.4.7) | 90.8% | 92.2% | 92.6% | 94.3% (90.0% 50-repo) | 88.9%–93.0% (All 4) | ~6.0% | Yes — All 376 HTML & JSON ↗ |
| Burp Suite Professional | ~75.2% | ~42.0% | — (None) | — (None) | Web/API only (No MCP/Mobile) | ~13.8% | No public report corpus |
| ProjectDiscovery Nuclei | ~24.5% (auth apps) | ~74.0% | ~51.0% | — (None) | Templates only (No Mobile/MCP) | ~6.8% | No benchmark report corpus |
| OWASP ZAP | ~58.4% | ~28.0% | — (None) | — (None) | Basic API/GraphQL (No MCP/Mobile) | ~21.5% | Synthetic WAVSEP table only |
| Tenable Nessus | ~34.0% | ~71.5% | ~76.0% | — (None) | — (None) | ~16.4% | Closed vendor claims |
| Semgrep (OSS / Free) | — (None) | — (None) | — (None) | 57.9% (157/271) | SAST rules only | ~15.2% | Published in our 50-repo test ↗ |
| SonarQube Community | — (None) | — (None) | — (None) | 33.2% (90/271) | SAST rules only | 37,953 noisy issues | Published in our 50-repo test ↗ |
Ready to level up your security testing?
Join security professionals worldwide. Our bots don't sleep — starting at $149/mo for Advanced, $399/mo for Pro.
See pricing
Monthly, annual, and lifetime tiers. Crypto and manual bank transfer accepted.
View plans →Create an account
Sign up to manage licenses, download builds, and try the live demo environment.
Sign up free →Operator courses
Structured paths for web, network, AD, mobile, and OSINT. Hands-on labs included.
Browse curriculum →Join the Insomnia Discord Community
Connect with penetration testers, red team operators, DevSecOps engineers, and the core Insomnia team. Get release drops in #insomnia-updates, discuss 75 Academy CTF tasks, share custom 1-day CVE modules, and get direct support.